Handshake-Level Isolation
Total Adblock helps reduce tracking scripts before they initialize, limiting some opportunities for identity-related signals to be added to advertising profiles.
Some trackers have shifted away from third-party cookies and toward identity-related signals. Here is how FedCM can raise privacy questions and how browser filtering may help reduce related tracking scripts.
The cookie is dying, but tracking isn’t. That’s the uncomfortable reality of the 2026 web. The same year browsers finally dismantled the third-party cookie pipeline, the surveillance economy quietly relocated — and it found a new home inside one of the tools built to protect you. If you use “Sign in with Google” or any federated login, you should understand how that convenience can be turned into a cross-site anchor.
This piece breaks down what changed, how the exploitation actually works at the protocol level, and what you can realistically do about it. Spoiler: clearing your cookies won’t help here.
For more than a decade, cross-site tracking leaned on a familiar toolkit: third-party cookies,
invisible tracking pixels, and hidden cross-origin <iframe> containers.
These worked because browsers let websites read and write storage across domains with little friction.
That era is closing. Privacy-focused browser defaults and content-filtering tools steadily choked off cross-site storage access. The decisive blow landed when major Privacy Sandbox initiatives — including Topics and Protected Audience — were shut down, removing the replacement infrastructure trackers had been counting on.
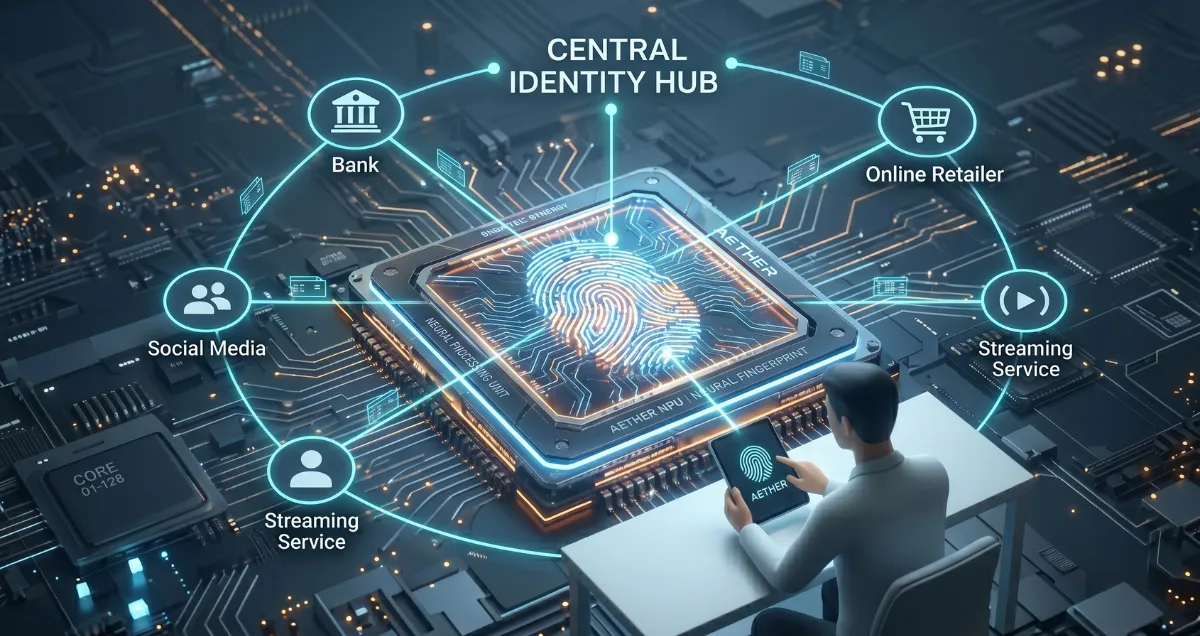
So the data economy did what it always does: it adapted. Rather than fight browser-level security head-on, trackers pivoted to the very APIs designed to replace cookies. Their new favorite anchor is the Federated Credential Management (FedCM) API — the system that powers native, browser-mediated logins like “Sign in with Google.” Built to eliminate invasive login iframes, FedCM has unintentionally become an ideal foundation for backend identity resolution graphs.
FedCM’s design intent is genuinely good. It removes the need for tracking iframes by inserting the browser as a neutral, secure middleman between an Identity Provider (IdP) and the website you’re visiting — the Relying Party. Instead of a login widget silently watching you across the web, the browser itself manages the credential handshake.
The problem isn’t the protocol. It’s who controls the endpoints. Data brokers and tracking syndicates realized that if you own infrastructure on either side of that handshake, the native flow can potentially be repurposed into a persistent identity signal. And because it runs through a sanctioned browser API, it wears the costume of legitimate security.
Here’s how the linkage typically executes — quietly, beneath the native interface.
This is what makes the technique so durable. Native identity mediation is now a core operational protocol for modern web authorization. That means surface-level privacy settings and incognito tabs cannot simply switch the API off without affecting common federated login flows across many parts of the internet. The exploit hides inside a feature you can’t comfortably live without.
The shift isn’t just a new trick. It’s a move to a different layer of the stack, which is exactly why old defenses miss it.
| Architectural Component | Legacy Cookie Tracking | Modern FedCM Exploitation |
|---|---|---|
| Execution layer | Application layer (iframe / JS) | Native browser protocol layer |
| User visibility | Invisible background cookie writing | Native browser prompts or silent handshakes |
| Network signal | Third-party cross-origin requests | First-party endpoint token routing |
| Privacy control challenge | Blocked natively by Safari / Firefox | May be treated as essential authentication traffic |
Read that last row carefully. The reason this approach is dangerous is that it routes through first-party endpoints and registers as legitimate authentication traffic — so the very filters that crushed third-party cookies tend to wave it through.
Defending against identity-graph linkage means abandoning the reflexes that worked against cookies. Clearing storage doesn’t touch it. Randomizing your canvas fingerprint or spoofing browser strings doesn’t either.
In fact, tampering with FedCM directly backfires. Because the flow depends on authentic, cryptographically verified tokens processed by the browser’s core networking engine, injecting “noise” into the handshake or faking user attributes won’t anonymize you — it’ll flag your account as fraudulent and get you blocked outright.
The sound defense operates earlier, at the code routing layer. The goal is execution containment: reduce a site’s client-side tracking tags or automated listeners before they initialize. Filtering unnecessary scripts can limit some background profiling while preserving legitimate logins.
For professionals and privacy-conscious users who want to protect their identity without sacrificing a fast, clean browser, the Total Adblock browser extension offers a focused line of defense. Federated logins themselves are a useful part of the modern web — the issue is the secondary analytics scripts engineered to exploit FedCM metadata and feed cross-site identity graphs, and those scripts originate from unauthorized data networks.
Total Adblock is built to filter ads, pop-ups, and known tracking requests. It parses web requests and blocks many connections to known data brokers, telemetry trackers, and real-time ad endpoints before they load in the browser. The result can be a cleaner workspace with fewer intrusive scripts. Users who spend time with streaming media get a bonus: the App strips out intrusive in-play video ads, leaving a cleaner, uninterrupted viewing experience.
It runs quietly in the background, with settings and trusted-site controls you can review. You retain control over your own list of trusted platforms while known tracking networks remain filtered.
The takeaway is a small but important correction to an old habit. Wiping your data still has its place — but the surface that matters now lives in how the browser authenticates, not what it stores. The cleanest defense is deciding, right at the edge of your own machine, who gets to join that handshake at all.
Disclaimer: This page is a paid advertorial. We may receive compensation if you follow instructions to purchase products mentioned in this article.
Total Adblock helps reduce tracking scripts before they initialize, limiting some opportunities for identity-related signals to be added to advertising profiles.
Filter lists help block many outbound connections to known data brokers, telemetry endpoints, and real-time ad servers in the browser.
The App runs quietly with simple settings. As a bonus, it can strip many intrusive in-play video ads for a cleaner viewing experience.
Click “Get the App” and review the current plan and permission details on the official Total Adblock page.
Follow the browser prompts to add the extension and review the default settings.
Browse with filtering enabled, and allowlist trusted sites if a page needs adjustment.
No. Federated logins are a legitimate part of the web, and the App leaves them intact. It targets the secondary analytics scripts that try to exploit identity metadata — not the authentication itself. You keep ordinary sign-in flows while reducing some related tracking scripts.
Performance varies by site. By cutting connections to many trackers and ad endpoints before they load, the App can reduce network activity and data usage on some pages.
Yes. You retain full authority over your own allowlist. Add any platform you trust in a couple of clicks, while corporate tracking networks stay blocked everywhere else.
Reduce tracking scripts that may piggyback on browsing and sign-in flows.
Get the App